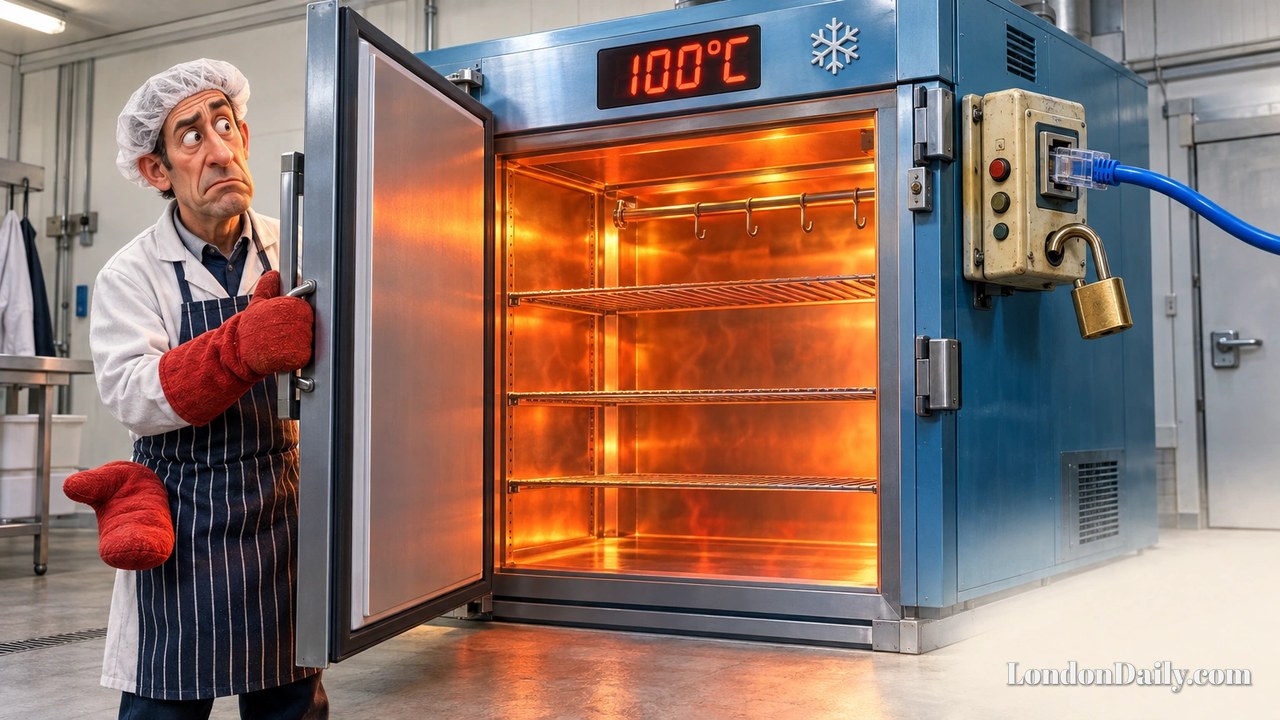
A cyber-attack that disrupted supermarket refrigeration across Europe has also hit British meat suppliers, with one business reporting cold units reaching 100C. The affected UK equipment was empty, so no produce was lost, according to the British Association of Independent Meat Suppliers (AIMS).
The association, which represents more than 300 businesses, said two other members had seen fridges unexpectedly begin defrosting. Spokesman Tony Goodger described the firms as “collateral” in the attacks and urged vigilance throughout the food supply chain.
The National Cyber Security Centre (NCSC) confirmed “a couple of instances where vulnerable technology had been exploited in the UK”. Its operations director, Paul Chichester, said on Tuesday that the impact remained minimal and officials were helping organisations close vulnerabilities before further exploitation.
Monday’s disruption affected around 40 Delhaize supermarkets in Belgium and Luxembourg, alongside smaller numbers of shops in Sweden, Ireland, the Netherlands, Estonia and Finland. Retailers discarded spoiled food, with some putting their losses at hundreds of thousands of euros.
Belgian refrigeration manufacturer Sabcobel said evaporators in affected units had been switched to defrost mode, causing temperatures to rise. The same method was thought to have been used in early October, when attacks on supermarkets and food suppliers across France targeted hundreds of stores overnight and spoiled produce estimated to be worth millions of euros.
Those earlier attacks exploited weaknesses in remote refrigeration-management systems that cyber-security researchers had identified months before. The practical danger is that access to these controls allows an attacker to disrupt the conditions keeping food usable.
Mathieu Tilman, who runs a Delhaize supermarket in Belgium, described the waste as “truly distressing”. He said: “There's so many people starving, people who don't have enough to eat. How can we end up throwing away so much food?”
NCSC chief executive Dr Richard Horne said staff had worked through the night to alert potentially affected UK organisations. On Tuesday, he said it was still “too early to say” who was responsible.
Horne warned that businesses had kept ageing systems beyond their useful lives without upgrading them or isolating them from the internet. He said artificial intelligence could help adversaries find and exploit weaknesses more quickly; he did not establish that it had been used in these attacks.
Graham Wynn of the British Retail Consortium said retailers invested heavily in cyber-security and were working with the NCSC to secure refrigeration. Horne’s wider message was that businesses needed to renew the technology they relied upon: the immediate UK losses may be limited, but exposed systems still require attention.
Join the conversation