London Daily

Focus on the big picture.
Saturday, Oct 03, 2026

Password manager Passwordstate hacked to deploy malware on customer systems

Password manager Passwordstate hacked to deploy malware on customer systems

A mysterious threat actor has compromised the update mechanism of enterprise password manager application Passwordstate and deployed malware on its users' devices, most of which are enterprise customers.

A mysterious threat actor has compromised the update mechanism of enterprise password manager application Passwordstate and deployed malware on its users’ devices, most of which are enterprise customers.

Click Studios, the Australian software firm behind Passwordstate, has notified its 29,000 customers earlier today via email.

According to a copy of the company’s communications, obtained by Polish tech news site Niebezpiecznik, the malware-laced update was live for 28 hours between April 20, 20:33 UTC and April 22, 00:30 UTC.

Danish security firm CSIS, which dealt with the aftermath of this supply chain attack, published today an analysis of the attacker’s malware. The security firm said the threat actor forced the Passwordstate apps to download an additional ZIP file named “Passwordstate_upgrade.zip” that contained a DLL file named “moserware.secretsplitter.dll.” After installation, this DLL file would ping a remote command and control server, from where it would request new commands and retrieve additional payloads.

While initially it was unknown what attackers collected from infected systems, in two updates [PDF, PDF] published after this article went live, Click Studios said the malware collected the following information and sent it back to its command and control server:

Computer Name, User Name, Domain Name, Current Process Name, Current Process Id, All running Processes name and ID, All running services name, Display name and status, Passwordstate instance’s Proxy Server Address, Username and Password

In other words, the password store was taken. According to the Australian company, the following information is typically included in the password table:

Title, UserName, Description, GenericField1, GenericField2, GenericField3, Notes, URL, Password

Although the company said “there is no evidence of encryption keys or database connection strings” were taken, Juan Andres Guerrero-Saade, Principal Threat Researcher at SentinelOne, pointed out on Twitter, that there are tools currently available that can decrypt the Passwordstate vaults and recover cleartext passwords.

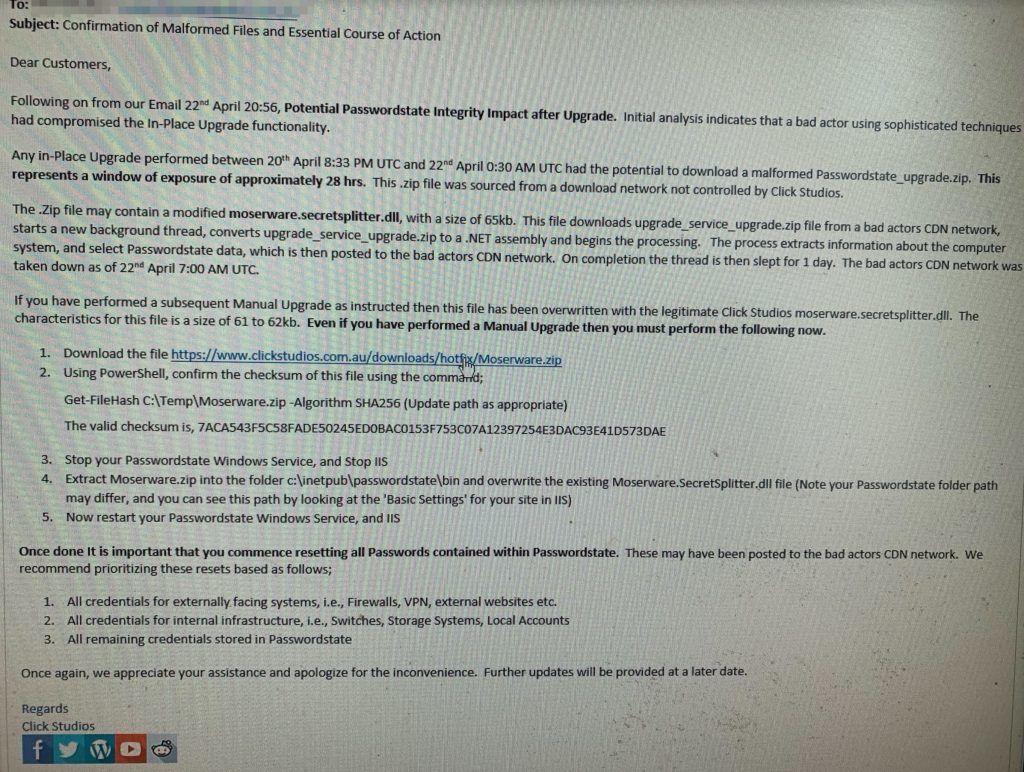
Click Studios released a hotfix package [ZIP] that would help customers remove the attacker’s malware, which the company named Moserware. [instructions are in the image above]

Click Studios said the hack took place after a threat actor compromised the “In-Place Upgrade functionality” of a CDN network not controlled by Click Studios. Only the company’s Windows client appears to have been modified to add malware in the attack.

29,000 companies now have to rotate passwords


In the aftermath of this security breach, the Australian firm has told customers to change all the passwords they stored inside compromised Passwordstate password managers as soon as possible.

Since this is a password manager is sold primarily in bulk to enterprises, to whom it is advertised as an on-premises system, changing passwords won’t involve just email and website accounts, but also passwords for internal gear such as firewalls, VPNs, switches, routers, network gateways, and others, which many employees would most likely have saved inside the app thinking it was a secure local storage system.

“This is a real annoying breach,” William Thomas, a malware analyst at UK security firm Cyjax, told The Record. “Imagine having to change all your passwords for each device on the network, on a Friday.”

Several network administrators have told The Record on Friday that they had to work over the weekend to change the passwords of all their IT inventory as a result of the breach. Many companies also intend to activate incident response plans to check logs for unauthorized access as a result of this incident as well, resulting in many overtime hours for their already swamped security personnel.

Comments
Darth Neo 3 year ago
This is hardly relevant. The event happened in 2021 and the vendor identified and took action within 28hrs. They have subsequently made major improvements to their software, including removing the previous method of updating. The issue affected Build 9117 and they are now on release 9823. I have to question the reasoning on reporting news that is over 2 years old and has been resolved promptly by the vendor.

Newsletter

Related Articles

0:00
0:00
Close
Church of England to Apologize for Role in Historical Forced Adoptions
UK Defence Ministry Investigates Historical Use of RAF Bases by Jeffrey Epstein
Scottish Housing Completions Fall to 11-Year Low
Welsh First Minister Calls for Expanded Devolution Settlement
UK Pledges £50 Million to Expand Domestic Military Drone Capabilities
UK Opens First Commercial Geothermal Plant in Cornwall
Green Party Wins Gorton and Denton By-Election as Labour Falls to Third
Prime Minister Andy Burnham Opens Review of UK-EU Relationship
UK Inflation Rises to 3.1%, Adding Pressure on Household Finances
UK Removes VAT From Domestic Electricity Bills to Ease Winter Energy Costs
Counterterrorism Police Arrest Sixth Suspect Over RAF Fairford Incident
UK Councils to Receive Sweeping Planning Powers to Ban New Vape and Betting Shops
Chancellor John Healey Faces Tax and Pension Scrutiny Ahead of Autumn Budget
Metropolitan Police Apologise for Accidental Disclosure in High-Profile Investigation
UK Universities Report Record International Enrolment as Housing Pressure Grows
UK Logistics Firms Monitor Rhine Disruption as Low Water Threatens European Supply Chains
UK Food Industry Warns Inflation Could Approach 7%
UK Introduces Vaping Duty and Mandatory Retail Stamps
Scotland Raises Property Taxes and Expands Child Payment in Annual Budget
Greggs Plans Four Factory Closures With 740 Jobs at Risk
OECD Raises UK 2026 Growth Forecast to 1.1%
UK Inflation Rises to 3.1% as Bank of England Faces Rate Debate
Andy Burnham Criticises Brexit and Says Rejoining EU Single Market Remains an Option
UK Imposes New Sanctions on Russian Military Networks and Propagandists
UK Launches Nationwide Early-Release Prison Scheme
Andy Burnham Says Security Services See Signs of Iranian Involvement in RAF Fairford Incident
Manchester City Found Guilty on Premier League Financial Charges After Independent Investigation
Scottish Court to Rule on Bid to Force No-Confidence Vote Against Aberdeen Council Co-Leader
UK Bans Extra Charges for Seating Children Under 12 Beside Accompanying Adults
UK Introduces Vaping Duty and New Licensing Requirements
Greggs to Close Four UK Factories and Cut 740 Jobs
Hundreds of Prisoners Released Early as England and Wales Prisons Reach 98% Capacity
UK Unveils New Russia Sanctions Targeting War Funding and Shadow Fleet
Burnham Says There Are Strong Indications of Iranian Involvement in RAF Fairford Security Breach
Prime Minister Andy Burnham Raises Prospect of Reviewing Britain's Post-Brexit EU Relationship
Markets Price in Bank of England Rate Increases as Inflation Rises to 3.1%
UK Borrowing Costs Climb Toward 5.5% as Global Bond Sell-Off Intensifies
UK-France One-In-One-Out Migration Agreement Expires as London Seeks Alternative Measures
Southwest England Faces Flood Alerts After Heavy Autumn Storms
UK Expands Funding for Rapid Electric Vehicle Charging Infrastructure
Welsh Government Approves Funding to Upgrade South Wales Transport
Northern Ireland Tensions Rise as Orange Order Rejects Drumcree Compromise
NHS Leaders Back Early Design of Proposed National Care Service
More Than One-Third of Regional UK Universities Face Financial Deficits
UK Current Account Deficit Narrows as Cross-Border Financial Flows Remain Strong
Bank of England and FCA Issue New Rules for Stablecoins and Digital Assets
MI5 Warns UK Universities Over Research Links With Chinese Institutions
UK Energy Price Cap Rises 4% as Electricity VAT Is Temporarily Suspended
Equity Calls for UK Personality Rights to Protect Performers From AI Replication
OpenAI Pauses Advanced Model Training Following Safety Concerns
×